𝟕 𝐄𝐬𝐬𝐞𝐧𝐭𝐢𝐚𝐥 𝐒𝐤𝐢𝐥𝐥𝐬 𝐓𝐨 𝐋𝐞𝐚𝐫𝐧 𝐅𝐨𝐫 𝐀𝐈 𝐅𝐨𝐫𝐞𝐧𝐬𝐢𝐜 𝐀𝐧𝐚𝐥𝐲𝐭𝐢𝐜𝐬
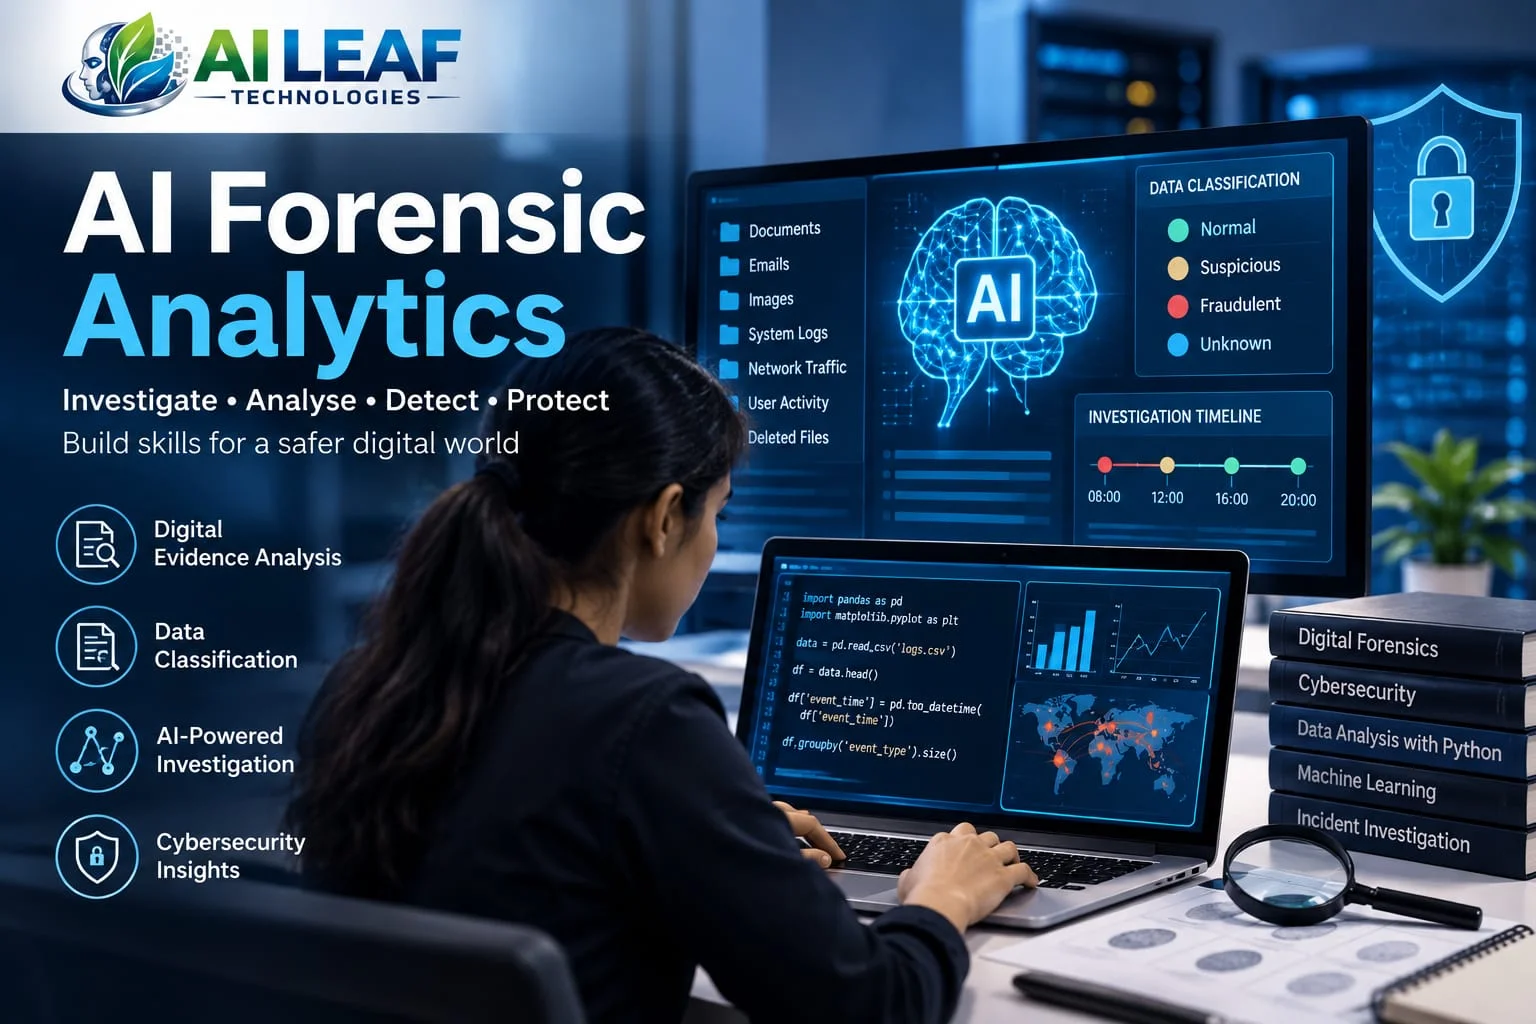
𝐖𝐡𝐚𝐭 𝐈𝐬 𝐀𝐈 𝐅𝐨𝐫𝐞𝐧𝐬𝐢𝐜 𝐀𝐧𝐚𝐥𝐲𝐭𝐢𝐜𝐬?
Digital investigations often involve examining large amounts of information collected from computers, mobile devices, networks, cloud platforms and other digital sources. Investigators must identify relevant evidence, understand what happened and document their findings in a reliable manner.
AI Forensic Analytics combines analytical methods and artificial intelligence techniques with digital forensic workflows. Depending on the application, AI can help organise information, identify unusual patterns, classify files or prioritise material for further examination.
Imagine an organisation investigating a suspected data breach. The security team may need to review system logs, file activity, account access records and network events. An analytical tool can help highlight unusual sequences or group related records, allowing investigators to focus their attention on potentially relevant evidence.
However, an unusual pattern does not automatically prove wrongdoing. Investigators must examine the underlying evidence, consider alternative explanations and validate their conclusions.
For students interested in artificial intelligence, cybersecurity or digital investigation, this field brings together technical knowledge, analytical thinking and responsible evidence handling.
𝐔𝐧𝐝𝐞𝐫𝐬𝐭𝐚𝐧𝐝𝐢𝐧𝐠 𝐃𝐢𝐠𝐢𝐭𝐚𝐥 𝐄𝐯𝐢𝐝𝐞𝐧𝐜𝐞
Digital evidence refers to information stored or transmitted in digital form that may be relevant to an investigation. Examples include system logs, email records, file metadata, application activity and network information.
The usefulness of digital evidence depends on more than finding a suspicious file or unusual event. Investigators must understand where the information came from, how it was collected and whether it has been altered.
A well-managed forensic process normally involves identifying relevant sources, preserving the original evidence, examining working copies where appropriate, documenting the methods used and reporting findings accurately.
AI can assist with parts of this process, but it cannot independently guarantee that evidence is complete, authentic or legally admissible. These questions depend on collection procedures, applicable rules and the circumstances of the investigation.
𝐒𝐞𝐯𝐞𝐧 𝐄𝐬𝐬𝐞𝐧𝐭𝐢𝐚𝐥 𝐒𝐤𝐢𝐥𝐥𝐬 𝐓𝐨 𝐃𝐞𝐯𝐞𝐥𝐨𝐩
𝐅𝐮𝐧𝐝𝐚𝐦𝐞𝐧𝐭𝐚𝐥𝐬 𝐎𝐟 𝐃𝐢𝐠𝐢𝐭𝐚𝐥 𝐅𝐨𝐫𝐞𝐧𝐬𝐢𝐜𝐬
Before using AI tools, learners need to understand how digital evidence is collected, preserved, examined and documented.
Study file systems, metadata, timestamps, evidence integrity and forensic documentation. Learn why investigators use controlled procedures and maintain records of evidence handling.
For example, a file’s displayed modification time may not tell the complete story. Time-zone settings, system configuration and other circumstances can affect interpretation. Investigators need to consider these factors before drawing conclusions.
𝐂𝐲𝐛𝐞𝐫𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐀𝐧𝐝 𝐍𝐞𝐭𝐰𝐨𝐫𝐤 𝐊𝐧𝐨𝐰𝐥𝐞𝐝𝐠𝐞
Cybersecurity fundamentals help learners understand attacks, unauthorised access, suspicious activity and security incidents.
Become familiar with authentication, access controls, network traffic, system logs, malware concepts and incident response. Understanding how systems normally operate makes it easier to investigate activity that differs from expected behaviour.
For example, an unusual login may result from a compromised account, but it could also reflect travel, a new device or a legitimate change in working arrangements. A security alert should be examined alongside related system activity and supporting evidence before deciding whether it indicates a genuine threat.
𝐏𝐲𝐭𝐡𝐨𝐧 𝐅𝐨𝐫 𝐃𝐚𝐭𝐚 𝐀𝐧𝐚𝐥𝐲𝐬𝐢𝐬
Python can help automate repetitive analytical tasks, process structured records and examine large datasets.
Learners can start with variables, functions, loops, file handling and basic error management. They can then explore suitable libraries for working with tables, timestamps and statistical summaries.
For instance, Python can help organise a sample collection of system logs by time, account and event category. The analyst can use the resulting summary to identify records that deserve further investigation.
Always work with authorised datasets and preserve original evidence according to the relevant forensic procedure.
𝐒𝐭𝐚𝐭𝐢𝐬𝐭𝐢𝐜𝐬 𝐀𝐧𝐝 𝐀𝐧𝐨𝐦𝐚𝐥𝐲 𝐃𝐞𝐭𝐞𝐜𝐭𝐢𝐨𝐧
Anomaly detection identifies observations that differ from an established pattern. In forensic analytics, it can help prioritise unusual events for additional review.
Learners should understand averages, distributions, variation, outliers and the limitations of statistical comparisons.
Consider a system that normally records a modest number of login attempts during working hours. A sudden increase overnight may warrant investigation. However, the change could also be caused by an automated backup, a software update or a legitimate operational event.
Anomaly detection provides a lead, not a final conclusion. Analysts should investigate the surrounding evidence before classifying an event as suspicious.
𝐀𝐈 𝐌𝐨𝐝𝐞𝐥𝐬 𝐀𝐧𝐝 𝐃𝐚𝐭𝐚 𝐂𝐥𝐚𝐬𝐬𝐢𝐟𝐢𝐜𝐚𝐭𝐢𝐨𝐧
AI models can help group information, identify patterns and prioritise records for review. Some systems can classify files or recognise similarities across large collections of material.
Understanding model evaluation is important. Learners should explore accuracy, precision, recall, false positives and false negatives.
A model may flag a harmless event as suspicious or overlook an important incident. The appropriate evaluation method depends on the investigation and the consequences of missing relevant evidence.
AI outputs should be recorded and assessed using a repeatable process. Analysts should document the evidence behind each result and clearly describe the reasons for prioritising it for further examination.
𝐃𝐚𝐭𝐚 𝐕𝐢𝐬𝐮𝐚𝐥𝐢𝐬𝐚𝐭𝐢𝐨𝐧 𝐀𝐧𝐝 𝐓𝐢𝐦𝐞𝐥𝐢𝐧𝐞 𝐀𝐧𝐚𝐥𝐲𝐬𝐢𝐬
Investigations may involve thousands of events spread across different systems. Visualisation can help organise this information into timelines, charts and relationship diagrams.
Practise organising datasets, tracing the order of recorded events and creating clear visual reports that accurately represent the available evidence.
For example, a timeline may show a sequence of account access, file downloads and system alerts. Investigators can compare these events with other reliable records to determine whether they are related.
Visual patterns can improve understanding, but the underlying records must remain available for verification.
𝐂𝐫𝐢𝐭𝐢𝐜𝐚𝐥 𝐓𝐡𝐢𝐧𝐤𝐢𝐧𝐠 𝐀𝐧𝐝 𝐄𝐯𝐢𝐝𝐞𝐧𝐜𝐞 𝐑𝐞𝐩𝐨𝐫𝐭𝐢𝐧𝐠
Technical findings are useful only when investigators can explain what the evidence shows and what it does not establish.
A good forensic report separates observed facts from interpretations, identifies the methods used and records relevant limitations. It should avoid unsupported claims and distinguish confirmed findings from possibilities that require additional examination.
Clear communication is especially important when reports are reviewed by security teams, management, auditors or legal professionals.
𝐇𝐨𝐰 𝐀𝐈 𝐒𝐮𝐩𝐩𝐨𝐫𝐭𝐬 𝐅𝐨𝐫𝐞𝐧𝐬𝐢𝐜 𝐈𝐧𝐯𝐞𝐬𝐭𝐢𝐠𝐚𝐭𝐢𝐨𝐧𝐬
AI can help investigators manage complex datasets by grouping similar records, highlighting unusual activity and assisting with information retrieval.
In a security incident, for example, analytical tools may help organise event logs from several systems. Investigators can use this information to develop a timeline and decide which records require closer examination.
AI-assisted text analysis may also help organise large collections of documents, subject to appropriate access permissions and privacy requirements.
The limitations are important. Incomplete data can produce misleading results, models can make classification errors, and generated summaries may omit significant details. Investigators should validate findings against original records and document the role of automated tools.
For established guidance on digital forensic practices, consult the National Institute of Standards and Technology’s official resource:
𝐀 𝐁𝐞𝐠𝐢𝐧𝐧𝐞𝐫-𝐅𝐫𝐢𝐞𝐧𝐝𝐥𝐲 𝐋𝐞𝐚𝐫𝐧𝐢𝐧𝐠 𝐑𝐨𝐚𝐝𝐦𝐚𝐩
Beginners can approach AI forensic analytics through a series of manageable learning stages.
𝐒𝐭𝐚𝐠𝐞 𝟏: 𝐋𝐞𝐚𝐫𝐧 𝐂𝐲𝐛𝐞𝐫𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐁𝐚𝐬𝐢𝐜𝐬
Understand operating systems, networks, authentication and common security incidents. These concepts provide the context needed to interpret digital activity.
𝐒𝐭𝐚𝐠𝐞 𝟐: 𝐄𝐱𝐩𝐥𝐨𝐫𝐞 𝐃𝐢𝐠𝐢𝐭𝐚𝐥 𝐅𝐨𝐫𝐞𝐧𝐬𝐢𝐜𝐬
Study evidence preservation, metadata, file systems, timestamps and documentation. For hands-on practice, work with simulated forensic cases or authorised datasets, ensuring that no real system is examined without explicit permission.
𝐒𝐭𝐚𝐠𝐞 𝟑: 𝐏𝐫𝐚𝐜𝐭𝐢𝐬𝐞 𝐃𝐚𝐭𝐚 𝐀𝐧𝐚𝐥𝐲𝐬𝐢𝐬
Learn Python and basic statistics. Practise organising sample event logs and producing clear summaries.
𝐒𝐭𝐚𝐠𝐞 𝟒: 𝐄𝐱𝐩𝐥𝐨𝐫𝐞 𝐀𝐈 𝐓𝐞𝐜𝐡𝐧𝐢𝐪𝐮𝐞𝐬
Learn how classification, anomaly detection and model evaluation work. Understand how false positives and false negatives affect investigation decisions.
𝐒𝐭𝐚𝐠𝐞 𝟓: 𝐁𝐮𝐢𝐥𝐝 𝐀 𝐒𝐚𝐟𝐞 𝐏𝐫𝐨𝐣𝐞𝐜𝐭
Create a project using synthetic system logs. Identify unusual patterns, compare the results with known sample events and document the limitations of your method.
This progression helps learners develop technical foundations before attempting complex investigations.
𝐄𝐭𝐡𝐢𝐜𝐬, 𝐏𝐫𝐢𝐯𝐚𝐜𝐲 𝐀𝐧𝐝 𝐄𝐯𝐢𝐝𝐞𝐧𝐜𝐞 𝐈𝐧𝐭𝐞𝐠𝐫𝐢𝐭𝐲
Digital investigations can involve sensitive personal information, confidential business records and legally significant evidence. Responsible handling is therefore essential.
Only access systems and datasets when authorised. Follow appropriate procedures for evidence preservation, maintain records of analytical actions and protect confidential information.
AI models should not be treated as independent authorities on guilt, responsibility or intent. Their outputs need contextual examination and appropriate human oversight.
When working on training projects, synthetic or properly authorised datasets provide a safer way to practise analytical techniques without exposing private information.
𝐂𝐡𝐨𝐨𝐬𝐢𝐧𝐠 𝐓𝐡𝐞 𝐑𝐢𝐠𝐡𝐭 𝐓𝐫𝐚𝐢𝐧𝐢𝐧𝐠 𝐏𝐫𝐨𝐠𝐫𝐚𝐦𝐦𝐞
Before choosing an AI forensic analytics course, examine the syllabus carefully. The programme should match your current experience and the type of work you want to pursue.
Look for coverage of digital evidence, cybersecurity fundamentals, data analysis, relevant AI methods and responsible investigation practices. If the course includes practical projects, ask which tools are used and whether the exercises take place in controlled training environments.
AI Leaf Technologies offers technology-focused training programmes. Contact the institute directly to confirm whether its current curriculum includes dedicated AI forensic analytics training, the exact syllabus and the available practical components before enrolling.
Explore the available programmes here:
𝐂𝐨𝐧𝐜𝐥𝐮𝐬𝐢𝐨𝐧
AI Forensic Analytics brings data analysis and artificial intelligence into digital investigation workflows. It can help organise large collections of records, identify unusual patterns and support the examination of digital evidence.
Developing the necessary skills requires more than learning an AI tool. Cybersecurity knowledge, Python, statistics, evidence handling, model evaluation and clear reporting all contribute to responsible analytical work.
Beginners can make progress by studying the fundamentals and practising with authorised or synthetic datasets. Carefully documented projects can help demonstrate technical understanding while reinforcing the importance of evidence integrity and independent verification.
For anyone considering training in this area, the next step is to compare relevant programmes and confirm that the syllabus includes the forensic and analytical skills required for the intended learning goals.
For course enquiries, contact the institute directly:
1. What is AI Forensic Analytics?
AI Forensic Analytics combines artificial intelligence and analytical methods with forensic workflows to help examine digital information, identify patterns and prioritise evidence for review.
2. Is AI Forensic Analytics the same as cybersecurity?
No. Cybersecurity focuses broadly on protecting systems and information. Forensic analytics focuses on examining information relevant to investigations, although the fields overlap.
3. Do beginners need Python for forensic analytics?
Python is useful for processing datasets, analysing logs and automating repetitive tasks. Beginners can start with programming fundamentals and practise using synthetic data.
4. How does AI help digital investigations?
AI can assist with classification, anomaly detection, information retrieval and prioritising records for further examination. Investigators must validate results against the underlying evidence.
5. What is digital evidence integrity?
Digital evidence integrity means maintaining and documenting evidence in a way that supports confidence that it has not been improperly altered. Appropriate collection and preservation procedures are essential.
6. What projects can beginners practise?
Beginners can analyse synthetic system logs, create event timelines, identify unusual activity and produce reports that explain their methods and limitations.
7. What should I check before joining a forensic analytics course?
Review the syllabus, practical exercises, tools, trainer experience, prerequisites and fees. Confirm that the programme covers the skills relevant to your goals.
8. Can AI alone prove that a security incident occurred?
No. AI-generated alerts and classifications require verification. Conclusions should be based on reliable evidence, appropriate investigation methods and human judgement.